
Hardware Security
Crypto Agility Csrc
Crypto-agility, also referred to as cryptographic agility, is the ability of a system to maintain up safety by rapidly adapting its cryptographic mechanisms, algorithms, and key management practices with out disrupting the the rest of the infrastructure. It requires the flexibleness to replace cryptographic parts like encryption, digital signature algorithms, or key trade protocols whereas maintaining data privacy and safety. Crypto-agility is the power of an organization’s techniques to switch cryptographic algorithms, keys, certificates, and protocols quickly and safely, without disrupting the methods that depend upon them. It is an operational functionality built from stock, abstraction, automation, and governance, not a single migration or a product you turn on. NIST describes it as a apply that organizations ought to adopt at every layer, from the algorithms themselves up through enterprise structure. Crypto-agility is the ability of an organization’s techniques to switch between cryptographic algorithms, keys, libraries, protocols, and certificates quickly and safely, with minimal operational disruption.
- The ISARA Corporation additionally emphasizes that cryptographic agiltiy permits organizations to evolve their cryptographic methods securely and with out disruptions, significantly lowering cryptographic risks while maintaining continuity 18.
- As we used a singular search string for Google scholar and the Google search engine, our search strategy could be reproduced.
- The completely different contexts of cryptographic agility, such asalgorithms, protocols, methods, or infrastructures point out a potential for furtherresearch to clarify the concepts in the cryptographic domain much more.
- Likewise, an HSM is incessantly assumed to be the place you go to enumerate certificates; it’s not.
Nice, But Is Crypto Agility An Pressing Priority?
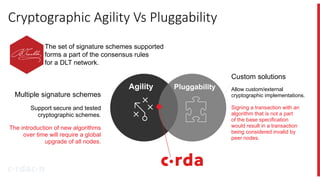
As we’ve illustrated the applicability of our definitions in Section IV-D1, we now supply a second definition of cryptographic agility, specific for the appliance context in order to make it extra concrete and accessible. Our systematization and new, clearer taxonomy provides a basis towards a commonunderstanding of cryptographic agility. We hope that our work will advance futureresearch on the varied dimensions of cryptographic agility and guide researchers andimplementers in future work on specific aspects and contexts of cryptographicagility. To improve our work even additional, we offer a second definition of cryptographicagility throughout the given common context of an software.
Cryptographic Agility, Explained
Consequently, a one-size-fits-all protocol resolution just isn’t possible in that context 36. Additionally it’s unclear how regulation and export management will deal with PQC sooner or later. In this paper, we systematize the concept of cryptographic agility by providing three analysis contributions. First, we evaluate current definitions throughout academic and grey literature, figuring out six distinct categories to distinguish every facet throughout the definitions. Second, we synthesize these insights to establish a complete, canonical definition of cryptographic agility.
Iv-c The Person Evaluation Of Cryptographic Agility
First, it’s needed to tell apart between cryptographic agility and interoperability. Second, when making an attempt to increase crypto-agility, one has to properly engineer and prioritize the exact requirements, especially when it comes to this distinction. In the medium time period, more complex options will observe which will allow for a single scheme like ML_KEM (aka. Crystals-Kyber 63, 64) to be exchanged or backed up by other PQC schemes. In the lengthy run we want to perceive if and how more modern key exchange agreement (see, e.g., 65, 66) may be carried out and deployed in a practical and secure method.
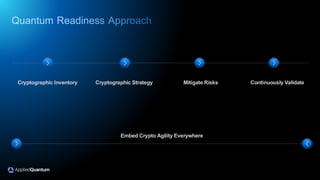
While this will introduce a language bias, our preliminary search recognized a limited variety of related studies in different languages, which we imagine doesn’t considerably affect the validity of our outcomes. Requirements like DES, MD5, and SHA-1, once thought of robust, had been ultimately weakened by advancing know-how and computing energy, forcing complicated and dear migrations. The framework and tools are provided “as-is” for educational and organizational use. Enable secure testing of recent algorithms in production environments through canary deployments and feature flags.

In April 2025, the CA/Browser Forum adopted Ballot SC-081v3 by a vote of 29 in favor and none opposed. The ballot sets a phased reduction within the most validity of publicly trusted TLS certificates and within the period for which domain-control validation could be reused. TrustFour’s structure is constructed to automate, monitor, and enforce these adjustments across your environment—helping you scale securely as threats and standards evolve. TrustFour embeds crypto‑agility as a basic capability, especially inside its T4 – Defend product, which is dedicated to workload attack surface protection and guaranteeing resilient cryptographic operations. Ampatzoglou et al. 70 point out that the dearth of repeatability, the dearth of coverage of research questions, the shortage of comparable related work and the shortage of generalizability threatens the validity of studies.
At Present there is a lack of clear common understanding of crypto-agility, bothin phrases of concrete practices and likewise on an abstract educational level21. Concepts from the classical world are sometimes notdirectly applicable to post-quantum, as they have been based on the idea thatthe totally different cryptographic schemes are considerably direct replacements for eachother. For occasion, when switching from RSA1024 to RSA2048 the precise changeson how to deal with the cryptography have been comparatively small, though notnegligible 45. On the other hand, changing RSA2048with a post-quantum scheme means there are a number of important pitfalls to keep away from. An necessary side of crypto agility is to speed up response instances considerably and reduce the potential for human error. Audit your tech stack to establish gaps in current tools that could derail progress and have them up to date.
Sincethose new algorithms are sometimes nonetheless too younger to supply the identical level of trust inthe soundness of their design and implementations as classical algorithms, protocoldevelopers usually mix them with established classicalalgorithms 26. This strategy preservescurrent safety requirements while offering the potential for post-quantum safety. Crypto-agility is the flexibility of systems to shortly adapt cryptographic algorithms, keys, and practices to deal with evolving threats with out disrupting operations. This functionality ensures sturdy data security, helps post-quantum cryptography, and meets dynamic compliance requirements. Achieving crypto-agility requires a sturdy technique, effective key administration, and centralized certificate lifecycle management. Embracing crypto-agility prepares organizations for a safe future, guaranteeing flexibility against emerging vulnerabilities.
Establish concrete backup plans and prearranged agreements with alternate vendors for crucial cryptographic infrastructure, significantly Certificates Authorities (CAs). This offers resilience in opposition to the failure or compromise of a primary cryptographic service supplier in case of adversities. Test the flexibility to carry out a fast CA migration and undertake vendor-neutral certificate life cycle management solutions.
Crypto-agility allows organizations to implement the newest requirements and shortly transition to safer algorithms each time essential with minimum disruption to enterprise operations. The transition to post-quantum cryptography is probably the most significant cryptographic migration in history, and it makes crypto agility a strategic imperative. The capacity of a system to modify between cryptographic algorithms with out major redesign, critical for quantum migration readiness. Which means methods https://www.internetling.com/category/computer-software-2 might want to monitor, validate, and adapt automatically as requirements evolve. Most organizations already rely on dozens of cryptographic parts scattered throughout systems and vendors.